No Bullshit Privacy Policy
Last updated: October 26, 2026
This is a privacy policy that is required by the EU General Data Protection Regulation (GDPR) . However, this is not just an ordinary privacy policy. Because we noticed that no one really knows what kind of privacy policy you have to write if you want to be GDPR compliant, and we didn’t want to pay thousands of euros to clueless consultants, we decided to write our own “No Bullshit Privacy Policy”.
This privacy policy identifies every bit of information that we have from our customers. In other words, after you have read this privacy policy, you should know exactly what information we save to our database, what kind of backups we take, and what information is transferred to third parties.
Table of Contents:
- TL;DR
- Who Collects Your Data?
- The Person in Charge of the Collected Data
- The Name of the Register
- The Data Sources of the Collected Data
- The Data Collected by the testwithspring.com Website
- The Data Stored in Database Backups
- The Data Collected by Our Sales Reporting Software
- Regular Transfer of Data
- Transfer of Data Outside the EU or EEA
- The Data Stored in Backups
- The Principles of Protecting the Collected Data
- Individual Rights
TL;DR
Who Collects Your Data?
Your data is collected by Koodikupla Oy. Koodikupla is a limited liability company that is owned by Petri Kainulainen . Its address is:
Koodikupla Oy (Business ID: 2748994-2)
Anteronkierto 11 B 17
71800 Siilinjärvi
Finland
The Person in Charge of the Collected Data
The person who is in charge of the collected data is Petri Kainulainen. His contact information is given in the following:
Petri Kainulainen
Anteronkierto 11 B 17
71800 Siilinjärvi
Finland
Email address: petri.kainulainen@koodikupla.fi
The Name of the Register
The customer and student register of the Test With Spring Course.
The Data Sources of the Collected Data
The data that is collected by Koodikupla Oy or sent to third parties, is either received from the user or determined from the data given by the user. The exact data sources of the collected data are described in the following sections.
The Data Collected by the testwithspring.com Website
This section describes the data that is collected by the testwithspring.com website.
Access Log
We use the Apache HTTP server that logs all requests processed by the server. These requests are written to a so-called access log. The access log contains the following data:
- The timestamp of the HTTP request
- The IP address of the client
- The value of the User-Agent HTTP request header
- The value of the Referer HTTP request header
- The requested resource
- The request method
- The used HTTP protocol
- The returned HTTP status code
- The size of the returned HTTP response
The collected data is extracted mainly from the incoming HTTP request. Also, before the Apache HTTP server returns the response to the client, it will extract the returned HTTP status code and the size of the returned response, and write this information to the access log.
We collect this data because we have a legitimate interest to prevent abuse.
We store old access logs for one month.
The Data Stored in Database Backups
Before we transformed this website into a static HTML website, we used WordPress and several WordPress plugins to serve content to our customers. This section describes the information that was collected by WordPress and the used WordPress plugins. This information is currently stored in database backups . The data that’s identified in this section is stored as long as the database backups.
If you want to take a look at a specific subsection of this section, you can use the following links:
- Blocked IP Addresses
- Comments
- Course Data
- Live Traffic
- Login Attempts
- Opt-In Forms
- Orders
- Testimonials
- User Accounts
Blocked IP Addresses
The Wordfence WordPress plugin provided additional protection for the testwithspring.com website. This plugin identifies malicious traffic and blocks IP addresses that send this traffic to this website. We can also block IP addresses manually by creating so-called block rules.
A block rule contains the following information:
- The IP address
- The country of the IP address
- A reason that explains why the IP address is blocked
- The creation time of the rule
- The expiration time of the rule
- The timestamp of the last request sent to this website
This data was extracted from the malicious HTTP request or given manually by an administrator. The country of the IP address was determined by using an IP location finder.
We collected this data because we had a legitimate interest to prevent abuse.
Comments
The students of the Test With Spring course could add new comments to the lessons published on this website. When a user published a new comment on this website, WordPress collected the following data:
- The IP address of the student.
- The username of the student.
- The email address of the student.
- The comment text.
- The creation time of the comment.
This data was given by the student. When a student submitted the comment form, they gave us their consent to collect this information and save this information to our database.
Course Data
We used Learndash as a learning management system (LMS). It collected the course data of each student. Learndash collected the following data:
- The packages purchased by the student
- Completed lessons
- Completed topics
- Completed packages
- The assignment answers
All information that was collected by Learndash was given by the students:
- When a student purchased a package of the Test With Spring course, Learndash saved this information to the database.
- After a student had finished a lesson or a topic, they could mark it as completed by clicking a button found from the user interface. A package was considered as completed if a student had finished all its topics.
- After a student had finished a lesson, they could answer the assignments given to the student.
We collected this data because we had a legitimate interest to:
- Ensure that a student can access only the lessons which belong to the purchased package.
- Help our students to track their progress.
- Provide assessment feedback to our students (add comments to their assignment answers).
Live Traffic
The Wordfence WordPress plugin provided additional protection for the testwithspring.com website. This plugin has a firewall that keeps track of the HTTP requests sent to the course’s website and blocks malicious HTTP requests.
Wordfence collected the following information:
- The timestamp of the HTTP request
- The IP address of the client
- The host name of the IP address
- The geolocation of the IP address (country)
- The value of the User-Agent HTTP request header
- The type of the HTTP request (human, bot, warning, blocked)
- The requested resource
- The returned HTTP status code
This data was extracted mainly from the incoming HTTP request. The country of the IP address was determined by using a local database. Also, the returned HTTP status code was extracted from the returned HTTP response.
We collected this data because we had a legitimate interest to identify and block malicious traffic.
Login Attempts
The Wordfence WordPress plugin provided additional protection for the testwithspring.com website. This plugin keeps track of login attempts and blocks login attempts if it suspects that someone is trying to log in by using a brute force attack.
Wordfence collected the following data:
- Timestamp
- The IP address of the client
- Username
- A boolean which is true if the user is an existing user and false otherwise.
- The outcome of the login attempt (success, failed).
This data was extracted mainly from the HTTP request which was sent to the testwithspring.com website when a user submitted the login form. The outcome of the login attempt and the boolean flag (existing user) were determined from the result of the login attempt.
We collected this data because we had a legitimate interest to prevent abuse.
Opt-In Forms
We implemented our opt-in forms by using the Thrive Leads WordPress plugin. This plugin gathered statistics about the conversion rates of our opt-in forms and stored the email address of every student who subscribed to our email newsletter.
Thrive Leads collected the following data when the user submitted an opt-in form.
- Timestamp
- Email address
- The lead group / short code which displayed the opt-in form
- The type of the Opt-In form
- The referrer URL
The collected information was given by the student when they subscribed to our email newsletter.
The email address was given by the student when they subscribed to our email newsletter. The lead group / short code and the type of the opt-in form were determined by Thrive Leads. The referrer URL was extracted from the incoming HTTP request.
We collected this data because we have a legal obligation (Article 7 of EU GDPR) to prove that a person had given us their consent to send email to them.
Orders
We used WooCommerce as our eCommerce platform, and it kept track of the orders made by the people who purchased this course. When WooCommerce created a new order, it saved the following information to the database:
- Customer
- Company name
- VAT identification number
- Name
- Address
- Email address
- Order
- Timestamp
- The purchased product
- The number of the purchased products
- VAT free price in USD
- VAT country
- VAT amount in USD
- Total price in USD
- The status of the order (completed, cancelled, refunded, failed)
- Payment
- Timestamp
- The IP address of the customer
- The used payment method
- The Stripe ID of the payment
This data was given by the student when they purchased this course. The payment information was provided by Stripe.
We collected this data because we had a legitimate interest to show the order history on the student’s profile page. This ensured that a student had an easy way for accessing their order history.
Testimonials
We used a WordPress plugin called Thrive Ovation that allowed us to gather testimonials from our students and show these testimonials on the testwithspring.com website.
Thrive Ovation collected the following information:
- The name of the student
- The email address of the student
- The occupation of the student
- The photo of the student
- The testimonial text.
- The change history of the testimonial. This change history answers the following questions:
- Who made the change
- What was changed
- When the change was made
This data was given by a student when they submitted the testimonial form. Also, we requested a photo from the student if they hadn’t provided it when they wrote the testimonial in question.
When a student submitted the testimonial form, they gave us their consent to collect the information given by them and save this information to our database. Also, before a testimonial was used in our marketing material, the student received an email which allowed them to either accept or reject the testimonial.
We collected this data because we wanted to collect feedback from our students and use this feedback in our marketing material.
User Accounts
When a student purchased this course, they had to also create a user account on our website. We collected the following information from each user:
- Username
- First name
- Last name
- Email address
- Password hash (bcrypt)
- User role
- The registration date
The collected data was given by the student when they purchased this course.
We collected this data because we had a legitimate interest to ensure that only authorized persons (our students) could access the material of this course.
The Data Collected by Our Sales Reporting Software
We also used an in-house reporting software that read data from Stripe and Taxamo . Our reporting software read the following data from Stripe and Taxamo:
- Taxamo
- Taxamo transaction ID
- Tax free price in USD
- VAT country
- VAT percentage
- VAT amount in USD
- VAT identification number (if given)
- Deducted VAT amount in USD (if VAT identification number was given)
- Refunded tax amount
- Price with VAT in USD
- Refunded total amount
- The status of the transaction
- Invoice place
- Woocommerce order ID
- Stripe
- The Stripe ID of the payment
- Payment amount in USD
- Refunded amount in USD
- Payment amount in EUR
- Refunded amount in EUR
- Stripe fee in EUR
- Payment description
- Payment status (paid, refunded)
- The amount that is paid to our bank account (in EUR)
The collected data is read from Stripe and Taxamo. However, it was originally provided by the student when they purchased this course or determined from the provided data.
We collected this data because we had a legitimate interest to automate the sales report creation process.
We store this data for ten years after the fiscal period in which the purchase was made has ended.
Regular Transfer of Data
This section identifies the information that was transferred to third parties at some point. If you want to take a look at a specific subsection of this section, you can use the following links:
Email List
We had an email list that allowed us to keep in touch with our customers. We used an email marketing tool called Drip for this purpose. Drip collected the following data:
- The email address of the student.
- The time zone of the student.
- The method that was used to subscribe to the newsletter.
- Tags which are used to segment subscribers to different groups. For example, a tag can identify the package purchased by the subscriber (starter, intermediate, and master).
- A list of emails sent to the student.
- A list of emails which were opened by the subscriber.
- A list of emails which contained a link that was clicked by the subscriber.
- A list of trigger links clicked by the subscriber.
- A list of subscribed email campaigns.
- Notes about the customer.
Drip collected its data by using the following data sources:
- Our student. The email address is provided by our student. When a student opens our email or clicks a link found from our email, Drip updates the open and click statistics of the email in question.
- Drip. A list of emails sent to the student is updated by Drip when we send a new email to the subscribers of our newsletter.
- An administrator. When a student subscribes to our newsletter, the administrator adds the correct tags to the student.
We used the collected data for three different purposes:
First, we sent course related notifications to our subscribers. These notifications included:
- Every time when a new lesson is added to the course or the information of an existing lesson is updated, we send an email to the students of the course.
- We notify the students of the course about upcoming maintenance breaks.
- We notify the students if our website is down.
- We send monthly webinar invitations to the students who have enrolled in the master package.
Second, we segmented our subscribers to different groups because this allowed us to send relevant information to our subscribers. For example, if we added a new lesson to the master package, we could notify only the students who can access it.
Third, we used the open and click rates for improving our communication. We wanted to provide useful information to our students and these two statistics helped us to achieve this goal.
We collected this data because the subscriber had given us their consent to do so. When a person subscribed to our email newsletter, they had to confirm their subscription by clicking the confirm link found from the confirmation email.
This data was stored as long as the subscriber is subscribed to the newsletter. When a subscriber cancelled their subscription, we stored this data for 30 days before it was deleted permanently.
Additional Information:
Mailgun
We used Mailgun (EU region) for sending the following emails:
- Instructions which describe how a student can reset their password.
- Order confirmations.
- Emails which contain the approval and rejection links of the testimonials written by our students.
When we sent email with Mailgun, we sent the following data to it:
- The email address of the sender
- The email address of the recipient
- The subject of the email
- The message body (not shown on the Mailgun log)
Mailgun added this information to its internal log (except the message body). This log contained also other information such as the delivery status of the email.
The collected data was given by the student when they purchased this course, started the password reset process, or wrote a testimonial. Also, an administrator might have made some changes to the actual testimonial text.
We sent this data to Mailgun because:
- A student had given their consent to do so when they submitted the testimonial form.
- We had a legitimate interest to ensure that the order confirmation emails and password reset emails were delivered to the inbox of the recipient.
This data was stored for 30 days.
Additional Information:
Payment and Accounting
Before we describe the information that was transferred to our payment and accounting partners, we explain how this information was collected.
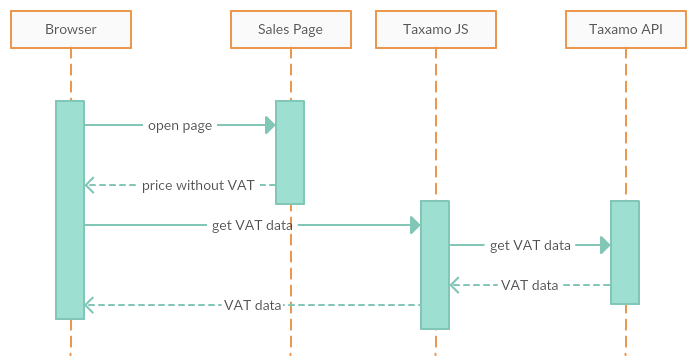
When a user opened our sales page, they started a sequence that had the following steps:
- The browser opened the sales page which had tax free prices.
- The browser queried the VAT data from Taxamo by using Taxamo’s JavaScript library (
taxamo.js). Before Taxamo could return the VAT data, the user’s country was detected by using IP geo-location. - After Taxamo returned the VAT data,
taxamo.jsreplaced the tax free prices with prices which include VAT.
The following figure illustrates this process:
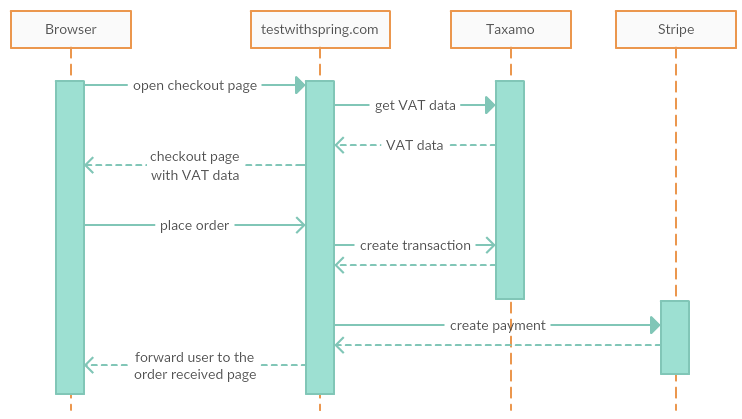
When a user clicked the buy button, they started a checkout sequence which consisted of the following steps:
- The browser requested the checkout page.
- The testwithspring.com website queried the VAT data from Taxamo. Again, before Taxamo could return the VAT data, it had to detect the user’s country by using IP geo-location.
- The testwithspring.com website returned the checkout page to the browser. Note that this page contained the VAT data returned by Taxamo.
- The user filled the checkout form and clicked the ‘Place Order’ button.
- The testwithspring.com website created a new Taxamo transaction and a new Stripe payment.
- The user was forwarded to the ‘Order Received’ page. This page displayed the information of the received order.
The following figure illustrates this sequence:
Note that we just described the happy path. If the user’s VAT country couldn’t be detected by using IP geo-location, they could set it on the checkout page. This meant that the VAT data would be fetched from Taxamo for the second time. Also, if the payment failed, the user could try again. If the user decided to do so, the testwithspring.com website created a new Taxamo transaction and a new Stripe payment.
Next, we will identify the information that was transferred to third parties. If you want to take a look at a specific subsection of this section, you can use the following links:
Taxamo
Taxamo (currently known as Vertex) allowed us to keep track of our sales and ensure that we were compliant with the European Union VAT rules for selling digital goods. Taxamo collected the following data:
First, if a user opened our sales page and didn’t purchase this course, only the IP address of the user was sent to Taxamo.
Second, Taxamo collected the following data when a person submitted the checkout form:
- Customer
- Name
- Email address
- The VAT identification number (if given)
- Address
- Country
- IP address
- Transaction
- Woocommerce order ID
- Order date
- The description of the purchase
- The type of the transaction (untaxed, eu-b2c, or eu-b2b)
- The status of the transaction (new, confirmed)
- Tax free price
- VAT country
- VAT percentage
- VAT amount
- Price with VAT
- Refunded amount
- Payment description
- Payment amount
- Payment timestamp
This data was either given by the student when they purchased this course or determined from the given data. For example, the VAT country, VAT percentage, and VAT amount were determined from the data given by our student.
We collected this data because we had the following legal obligations:
- We must display the price that includes VAT on our sales page because this is required by the consumer protection act.
- We used this information as a voucher that identifies the transaction. This is required so that we can fulfill our legal obligations concerning accounting.
- We collected this information because we have to identify the customer’s location. We had to do this because the European Union VAT rules for selling digital goods required that we pay the VAT to the country in which the course is consumed. In other words, Taxamo helped us to calculate the VAT charged from the customer and store the evidence that allowed us to pay the VAT to the correct country.
Relevant Laws:
- Section 8 of the chapter 2 of the consumer protection act (20.1.1978/38) . Note that the English translation of this act is also available.
- Section 5 of the chapter 2 of the accounting act (1620/2015) .
- Chapter 12 a of the value added tax act (30.12.1993/1501) . Note that the English translation of this act is also available.
We have to store this data for ten years after the fiscal period in which the purchase was made has ended.
Additional Information:
Stripe
Stripe is a payment gateway that allowed us to accept credit card payments from our customers. Stripe collected the following information when a user submitted the checkout form:
- The information of the customer
- Name
- Email address
- Address
- The information of the payment
- Timestamp
- Woocommerce order ID
- Description
- Amount
- Stripe processing fee
- Net amount
- Refunded amount
- The result of the Stripe risk evaluation
- The status of the payment (successful, failed, refunded)
- The information of the used credit card
- Card number (only the last four digits are visible to us).
- The card verification code
- The card fingerprint
- The name of the card holder
- The expiration date
- The type of the card
- The origin country
- The result of the CVC check
- The result of the street address check
- The result of the ZIP code check
- The information of the used payment instrument (aka source)
- A unique source ID
- The type of the payment instrument (ach_credit_transfer, ach_debit, alipay, bancontact, bitcoin, card, eps, giropay, ideal, multibanco, p24, sepa_debit, sofort, or three_d_secure)
- The status of the payment instrument (canceled, chargeable, consumed, failed, or pending)
- The authentication flow that was used to create this source (redirect, receiver, code_verification, none)
- Usage (reusable or single_use)
- Creation time
This data was either given by the student when they purchased this course or determined from the given data.
We collected this data because of these two reasons:
- We had a legitimate interest to accept credit card payments from our customers and protect our customers from credit card fraud
- We had a legal obligation to use this data as a voucher that links the payment to the Taxamo transaction.
Relevant Laws:
We have to store this data for ten years after the fiscal period in which the purchase was made has ended. However, keep in mind that Stripe has its own legal obligations and these obligations define the real retention period of the collected data.
Additional Information:
Accountant
We have outsourced our accounting to an accounting firm. We sent a sales report to the accounting firm once a month. This report contains the following information:
- Woocommerce order ID
- Sales date
- Sales amount in USD
- VAT identification number
- VAT country
- VAT percentage
- VAT amount in USD
- Total sales amount in USD
- Refunded VAT amount in USD
- Refunded total amount in USD
- Total sales amount in EUR
- VAT amount in EUR
- Refunded total amount in EUR
- The Stripe fee in EUR
- The amount that is paid to our bank account (in EUR)
This data was created by our sales reporting software.
We sent this data to the accounting firm because the accounting firm helps us to fulfill our legal obligations regarding accounting and taxes. The accounting firm uses this information for two purposes:
- They do our bookkeeping.
- They do our VAT reports and send them to the tax authorities.
Relevant Laws:
- Accounting act (1620/2015) .
- Chapter 12 a of the value added tax act (30.12.1993/1501) . Note that the English translation of this act is also available.
This data is stored for ten years after the fiscal period in which the purchase was made has ended.
Youtube
We used Youtube for broadcasting the live webinars. Also, webinar replays and bonus lessons were uploaded to Youtube and embedded on the testwithspring.com website.
When a user watched a live webinar, webinar replay, or a bonus lesson, Youtube collected the following data:
- The IP address of the user
- The watched live feed or webinar
- The watch time
- The identity of the user. If a user is logged in to their Google account, Youtube will know what videos they are watching. If a user is not logged in to their Google account, Google might identify the user by using its tracking cookies.
This data was collected from the students who had purchased the master package.
We collected this data because we wanted to provide the bonus lessons to our students and share the webinar replay with students who couldn’t attend the live webinar. Also, the student had given us their permission to collect this data when they purchased the master package.
This data was stored indefinitely.
Additional Information:
Wistia Video Platform
We hosted our videos on Wistia’s video platform . Because we used Wistia’s privacy mode, Wistia didn’t collect any personally identifying viewer data. This meant that the Wistia player anonymized IP addresses, and disabled both session and cookie tracking.
Wistia collected the following analytics data when a user watched one of our videos:
- The anonymized IP address of the user.
- The location of the user. This information is determined by using IP geo-location. Note that Wistia cannot collect the exact location of the user because the IP address is anonymized.
- The internet service provider of the user. This information is determined from the IP address of the user.
- The operating system used by the user.
- The browser used by the user.
- The device used by the user.
- The watched video.
- A heat map which identifies the watched sections.
There were two things which we didn’t do:
- We didn’t track the email addresses of the people who watched our videos. Wistia has a feature that would have allowed us to do this, but we didn’t use it because we didn’t want to violate the privacy of our users.
- We didn’t use the Google Analytics integration provided by Wistia.
This data was collected from the students of this course.
We collected this information because we wanted to provide interesting content to our students. Also, the student had given us their permission to collect this data when they purchased this course.
This data is stored indefinitely.
Additional Information:
Transfer of Data Outside the EU or EEA
The following data was transferred outside the EU or EEA:
- The data collected by Drip . Drip is a U.S. company and the data that is collected by it is processed in the United States or any other country in which Drip or its subsidiaries, affiliates or service providers maintain facilities.
- The data collected by Stripe . The entity that provides services in Europe is Stripe Payments Europe that is located in the Republic of Ireland. However, the collected data may be stored and processed in any country where Stripe or its service providers have operations.
- The data collected by Youtube . Google is a U.S. company and the data that is collected by it is processed in the United States or any other country in which Google or its subsidiaries, affiliates or service providers maintain facilities.
- The data collected by Wistia . Wistia is a U.S. company and the data that is collected by it is processed in the United States or any other country in which Wistia or its subsidiaries, affiliates or service providers maintain facilities.
The Data Stored in Backups
Database Backups
We took periodic backups of the database of the testwithspring.com website. These backups contain all data that was collected by the testwithspring.com website . Currently we store only the latest backup that was taken before the “old” website was taken down.
We store this backup because:
- We want to fix the possible issues found from the content of the lessons.
- We must be able to fulfill our obligations defined by GDPR .
Other Backups
We took periodic backups of the data we needed to fulfill our legal obligations concerning accounting. These other backups contain the following data:
- Sales reports
- The data transferred to Taxamo
- The data transferred to Stripe
- The data transferred to the accountant
We took these backups because this material is the “source material” that is used to do our bookkeeping, and we have a legal obligation to keep it safe.
Relevant Laws:
- Section 5 of the chapter 2 of the accounting act (1620/2015) .
- Chapter 12 a of the value added tax act (30.12.1993/1501) . Note that the English translation of this act is also available.
These backups are stored for ten years after the fiscal period in which the backup was made has ended.
The Principles of Protecting the Collected Data
This section describes the principles which we use to protect the data that is collected by us.
The testwithspring.com Website
The data that was collected by the testwithspring.com website was protected by following these rules:
- All communication between a web browser and the testwithspring.com website used HTTPS. Every user (either a student or an administrator) had a username and a password that were used to log in to the course website. This password was hashed with bcrypt.
- A student could access only their own information.
- The testwithspring.com website had a firewall that protected it from malicious traffic and blocked brute force attacks.
- The testwithspring.com website used a malware scanner that performed regular malware scans.
- The testwithspring.com website sent automatic email alerts to the administrator when a WordPress plugin update was available.
- Only the administrator of the Test With Spring Course had the required permissions to access all information stored in the database of the testwithspring.com website.
- The information was saved in a database that was protected with a username and password. Only the administrator of the Test With Spring Course had access to this database.
- The database server and web server were located in Finland at locked and guarded premises. Only authorized personnel were allowed to access these premises and the information stored on these servers.
Manual Processing
When we process the collected data manually, we follow these principles:
- We minimize the number of persons who can access the collected data. At the moment only one person (Petri Kainulainen) can access it.
- We use two factor authentication every time when it’s supported by the service that stores the data described in this privacy policy.
- All communication between the administrator and a remote system happens by using HTTPS.
- All backups are stored in an encrypted hard drive.
- If a file is transferred to cloud storage, it is encrypted before it is transferred.
Automatic Processing
When the collected data was processed automatically, we followed these principles:
- Sensitive information (such as a password or a credit card number) was never written to a log file.
- All communication between the testwithspring.com website and an external system used HTTPS.
- All HTTP requests sent to external systems were authenticated by using the authentication mechanism supported by the external system.
Individual Rights
You have the right to access your personal data that has been collected by us. You can obtain a copy of your personal data by sending a signed letter to the person who is in charge of the collected data . This letter must contain the information that allows us to identify you. You can obtain your personal data free of charge once per year. Your request is processed within 30 days of receiving your letter.
You have the right to rectify incorrect data or complete incomplete data. If you want to exercise this right, you have to contact the person who is in charge of the collected data . Your request is processed within 30 days.
You have the right to have your personal data erased. You can have your personal data erased by sending a signed letter to the person who is in charge of the collected data . This letter must contain the information that allows us to identify you. Your request is processed within 30 days of receiving your letter.
You have the right to restrict the processing of your personal data. If you want to restrict us from processing your personal data, you have to send a signed letter to the person who is in charge of the collected data . This letter must contain the information that allows us to identify you. Your request is processed within 30 days of receiving your letter.
You have the right to data portability. This means that you can obtain the collected data in a machine readable format. You can obtain a copy of your personal data in a machine readable format by sending a signed letter to the person who is in charge of the collected data . This letter must contain the information that allows us to identify you. Your request is processed within 30 days of receiving your letter.
You have the right to object to the data processing based on legitimate interest, direct marketing, and data processing for purposes of scientific/historical research and statistics. If you want to exercise this right, you have to contact the person who is in charge of the collected data . Your request is processed within 30 days.
Also, if you think that we are processing your personal data in a way that breaks the law, you have the right to file a complaint with the office of the data protection ombudsman .